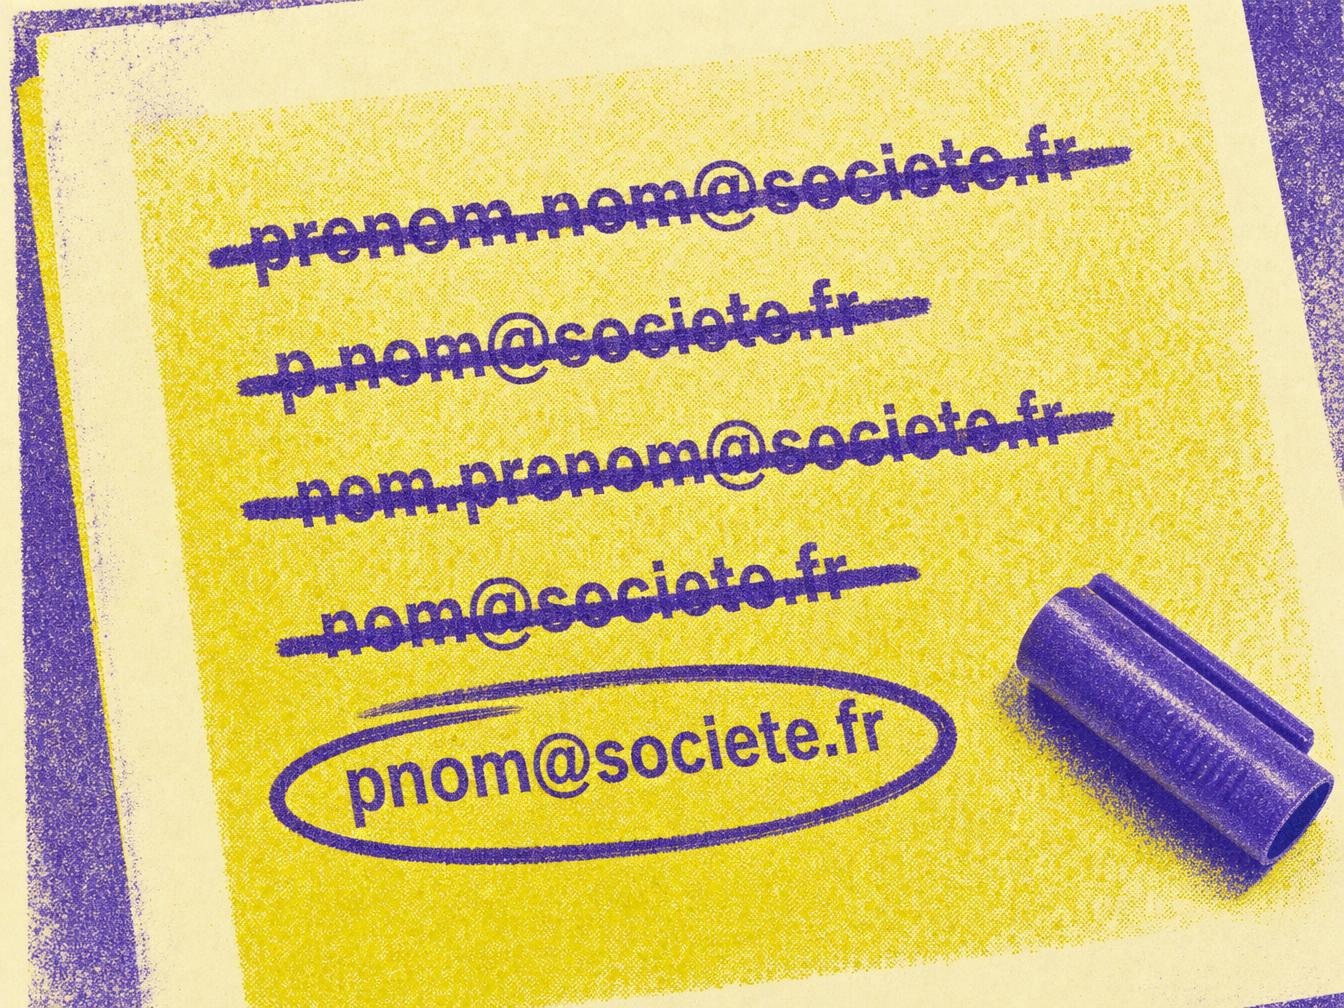
First.last@, f.last@, last.first@: how many variants does a prospecting tool try before an address responds? Does the person being targeted know anything about it? On the sender side, the symptom is familiar: campaigns that land in spam with no one knowing why, and a hard bounce rate that climbs on contacts that were “found” rather than collected.
Prior consent is not required by default. In its guidance of October 16, 2026, the CNIL (the French data protection authority) accepts legitimate interest as a basis for reconstructing a business email address, case by case: the person must be able to expect it, and the address is kept only if an actual first contact takes place within a reasonable time. An objection closes the door for good. Without these conditions, what remains is consent or abstention.
Address reconstruction according to the CNIL
Two public addresses at the same company follow the pattern “firstname.lastname@company.fr”, while the third team member has published no address. Applying the pattern to their name is address reconstruction. The CNIL describes it as deducing an address from a person’s name and their employer.
The guidance, titled “Reconstitution of professional email addresses: what framework is authorized?”, cites two uses: a prospecting database or a one-off contact in institutional relations. A name tied to an employer identifies someone, so the GDPR (applicable since May 25, 2018) applies.
Why isn’t consent required from the start?
The most natural legal basis is legitimate interest, Article 6.1.f of Regulation (EU) 2016/679, the GDPR. Reconstruction serves a main processing activity, often B2B prospecting, and can rely on the same basis. The CNIL sets a limit in one phrase:
“neither automatic nor systematic” (CNIL, guidance of October 16, 2026)
The analysis weighs the organization’s real interest against the impact on the person’s rights, then adds the question of what that person can reasonably expect. The reasoning is done case by case, and the organization must be able to justify it.
The guidance offers a method of analysis, not a scale. Growth Hacker’s analysis of B2B prospecting covers cold calls and guessed emails from the prospecting side; this article stops at reconstruction itself.
When the person doesn’t expect to be reached this way
A contact form in place of an address, or a profile whose privacy settings have been tightened: the CNIL reads both as signals of refusal.
A person with no identifiable online presence, or who has protected their contact details and points to a form, cannot reasonably expect to have their address reconstructed. In principle, they fall outside the scope. These signals are checked before producing the address, so before any send.
A gray area remains: a half-filled profile, an address published in 2019 and never updated. No mechanical threshold settles these cases.
Retention, information and objection
The address is kept only if an “actual first contact” takes place within a reasonable time. The October 16, 2026 guidance does not put a number on that delay. The organization that prospects therefore sets its own purge period for addresses that stayed unanswered, and documents it.
On information, the address was not obtained from the person: under the GDPR, Article 14.3.b requires telling them where the data comes from and how to object, at the latest at the first communication. The first email of the sequence is the last possible moment; Article 14.3.a sets a one-month ceiling in any case. A sentence like “your address was deduced from the format of your company’s addresses” is enough to name the source; it must come with the means to refuse.
Objection, a right granted by Article 21 of the GDPR for prospecting, excludes the person from any future reconstruction, without their having to justify it. Deleting the address is therefore not enough, since the same pattern would regenerate it at the next import. A companion CNIL page, “Reconstitution of professional email addresses: what are your rights?”, is addressed to the people concerned: the two texts are read together. A permanent objection list, reduced to the strict minimum needed to recognize the person, is the practical condition of this guarantee. Public authorities have a basis of their own, the “public interest task” (Article 6.1.e), with the same safeguards.
The message sent afterward
Sending falls under the prospecting rules: for a professional, Article L.34-5 of the French Postal and Electronic Communications Code governs the send, and the CNIL does not require prior consent if the message relates to their role, provided you inform them and give them a simple way to unsubscribe. Our article on GDPR in email marketing covers proof and unsubscription in detail.
The CNIL sheet is a French reading of the GDPR and changes nothing in other countries. In the United States, the CAN-SPAM Act sets no prior-consent requirement: every commercial message needs a working opt-out honored within 10 business days and a valid physical postal address, and the FTC compliance guide states that the law makes no exception for business-to-business email.
A source disclosure fits in one line, for example “Your address was deduced from the format of your company’s public addresses; reply STOP to stop being contacted”. If the sequence also measures opens with a pixel, the CNIL’s recommendation on open-tracking pixels sets its own conditions, separate from those of reconstruction.
The LinkedIn Sales Navigator case
Sales Navigator shows a person’s name and their job at a company, with no email address. The tool alone reconstructs nothing. The extensions plugged into it extract profiles and guess the address.
They run into two obstacles. LinkedIn’s user agreement forbids automated extraction. The criteria of the guidance apply to each person extracted. The CNIL fined the company Kaspr on December 5, 2024 (€240,000, decision made public on December 19) for collecting the contact details of LinkedIn members who had restricted their visibility. According to the CNIL, this collection exceeded what members of a professional network can reasonably expect: the same logic of reasonable expectation as in the guidance. The legal framework for scraping social data is covered in a separate article.
Responsibility is shared. The publisher of an extension or an email lookup service decides for itself to collect and store the contact details of the people targeted. In the Kaspr decision, the CNIL treats it as the controller of that file. It holds against it the lack of a valid legal basis and late information to the people concerned, and judges its data retention excessive. The sales team that uses it remains responsible for its own sends: it justifies its legitimate interest and informs the person from the first message. The contract signed with the tool shifts none of these obligations. The Kaspr decision is the only CNIL sanction cited here, and it targets the tool’s publisher. The contractual risk comes from elsewhere: LinkedIn has taken scraping providers to court. Proxycurl had to delete the data it obtained and stop accessing it under a permanent injunction; ProAPIs was accused in October 2025 of creating millions of fake accounts to siphon off profiles.
Tools that reconstruct or extract addresses are not all equal. The table reflects what each vendor says about its method on its own pages (as of October 21, 2026), except for Kaspr, Proxycurl and ProAPIs, documented above. None is illegal by nature: the fragility depends on where the data comes from and on how the sender uses it. The CNIL guidance does not cite any of these tools.
| Tool | How the address is obtained | Weak point |
|---|---|---|
| Hunter | Deduces the address from the company’s format and from addresses found on the public web; claims to use no third-party database. | Maintains a suppression list: a removed address does not come back through collection or deduction. The user remains responsible for their use. |
| Dropcontact | Generates and tests addresses with its own algorithms, with no third-party database according to the vendor. | Compliance argument from the vendor, unverified. The criteria of the guidance apply to whoever uses it. |
| lemlist | Looks up the address in a cascade across several providers. Its Chrome extension sends the profiles of a Sales Navigator search into a campaign. | The origin of the data gets lost in the cascade. The extension runs up against LinkedIn’s agreement. |
| Snov.io | Chrome extension on profiles and Sales Navigator searches, deduction by address format then verification, database advertised at 500 million addresses. | Extraction from LinkedIn: LinkedIn’s agreement and the reasonable expectation criterion. |
| Evaboot | Exports Sales Navigator searches in one click then looks up the address. Says it uses no database and caps exports per day. | Automated extraction from Sales Navigator, the very case targeted by LinkedIn’s agreement. |
| PhantomBuster | Automates actions and extractions on LinkedIn using the user’s session. | Its own blog speaks of a gray area and leaves responsibility for use to the user. |
| Waalaxy | Cascade of providers (BetterContact, FullEnrich, then Dropcontact according to its January 2026 article). | You must be able to tell the person where the address comes from (Art. 14), which the cascade complicates. |
| Lusha | Community of users who share their email signatures, licensed directories, public sources. Says it does not scrape social networks. | Relies on legitimate interest, with an opt-out form and a suppression list. |
| Apollo | Network of contributors, public web crawling and third-party providers. | Relies on legitimate interest. Data already exported remains, according to the vendor, the customer’s responsibility. |
| Kaspr | Extension displaying the contact details of LinkedIn profiles. | €240,000 fine from the CNIL (December 5, 2024) for collecting profiles with restricted visibility. |
| Proxycurl, ProAPIs | LinkedIn profile extraction services. | Sued by LinkedIn on contractual grounds (Proxycurl in January 2025, ProAPIs in October 2025). |
In practice, a few targeted public profiles, contacted quickly with a source disclosure, remain defensible under the 2026 guidance, to be assessed case by case. Entire lists extracted and then sent in an automated sequence are fragile: nothing in them checks for signals of refusal. Retention without a first contact becomes the norm.
Does address verification settle the question?
No. An SMTP test sends no email. Yet the address has already been produced from personal data, so the legal basis and informing the person still have to be established beforehand. Verification limits bounces and says nothing about compliance.
On the technical side, an address guessed on a domain that doesn’t have that mailbox comes back with error 550 5.1.1 (unknown recipient, a code defined by RFC 3463), reported by a non-delivery notice: it is a hard bounce. Repeated attempts across variants produce them in a chain. Gmail and Outlook, like other mailbox providers, factor these bounces into the sending domain’s sender reputation; the effects then show up in Google Postmaster Tools. The usual objection, “can’t we just filter afterward?”, falls flat: the bounce is already counted by the time you see it.
Another trap is catch-all domains: they accept any message addressed to the domain. A guessed address looks valid there in a test, with no guarantee that a human reads it. How catch-all domains work explains why these addresses are kept separate in serious list hygiene. Email Finder vs Email Verifier details the difference between finding an address and verifying it.
Before your next campaign on a reconstructed list, run a sample of 200 addresses through verification and compare its hard bounce rate with that of the addresses you collected from the people themselves.
A guessed address is still someone’s name.