Email marketing law in France rests mainly on one article of the Postal and Electronic Communications Code, L34-5, which sets an administrative fine of up to €375,000 for a company when the competition and consumer authority acts. The GDPR adds its own ceiling of €20 million or 4% of worldwide turnover for consent failures. This guide, checked against the official texts on 28 October 2026, sets out who needs to consent, what each message must contain, what changed for tracking pixels in 2026 and what a breach costs.
Which texts make up email marketing law in France?
Three layers apply at once. Article L34-5 CPCE is the national rule: it forbids prospecting by email to a natural person who has not given prior consent, and its current wording comes from law no. 2020-901 of 24 July 2020. This guide covers French law only. The ePrivacy directive (Directive 2002/58/EC of 12 July 2002) is the European source, and its article 13 requires prior consent for natural persons, allows the customer exception and requires Member States to ensure that the legitimate interests of subscribers who are not natural persons are sufficiently protected (article 13.5). The GDPR (Regulation (EU) 2016/679, applicable since 25 May 2018) governs the personal data itself: lawful basis, information, proof and individual rights.
Three authorities share enforcement of L34-5: the CNIL, the French data protection authority; the authority in charge of competition and consumer affairs, which imposes the €75,000 and €375,000 administrative fine written into the article; and the telecoms regulator Arcep. The CNIL and Arcep sanction under their own powers, with ceilings that this article does not cover. The same article also covers SMS, fax and automated calls.
Who must consent: B2C and B2B side by side
Individuals must consent before the first message. For a professional it depends on whether the email concerns their job, and generic addresses sit outside the rule. The table summarises the CNIL guidance on commercial prospecting by email, updated on 10 June 2026.
| Recipient | Legal basis | What you need | Where it stops |
|---|---|---|---|
| Individual (B2C) | Prior consent, L34-5 | Free, specific, informed and unambiguous consent given by a positive action; unticked box | Accepting general terms of use is not enough; consent can be withdrawn at any time |
| Existing customer | Customer exception, L34-5 | A prior sale or service, similar products of the same company, information at collection, simple free opposition at collection and in every message | Creating an online account without buying anything does not make someone a customer |
| Named professional (B2B) | Legitimate interest | A message related to the recipient’s profession, information at collection, simple free opposition | An offer unrelated to the job does not meet the CNIL condition |
| Generic address (contact@, info@) | Outside the principles | No prior consent | No specific rule on the CNIL page |
The CNIL also accepts legitimate interest for non-commercial prospecting, such as by a charity, provided people were told at collection that their address would be used for it.
A double opt-in is the cleanest way to document the B2C case; our guide to double opt-in covers the setup. For B2B addresses built from a name pattern, see what the CNIL says about guessing a business email address.
What every commercial email must contain
L34-5 sets three requirements for every prospecting message. The CNIL guidance adds a fourth on how to refuse.
- Valid contact details the recipient can use to ask for the mailings to stop (law).
- An honest sender identity, never hidden (law).
- A subject line related to the offer (law).
- A simple means to refuse future messages in the message itself, such as a one-click unsubscribe link (CNIL guidance).
Collecting addresses and proving consent
A pre-ticked box is forbidden; the CNIL recommends an unticked box by default. The sentence “by registering you accept commercial offers” buried in general terms fails for the same reason. At the moment of collection you must tell people their address may serve prospecting and give them a simple, free way to object.
Proof is on you. Article 7(1) of the GDPR says that where processing rests on consent, the controller must be able to demonstrate it. In practice that means keeping the form wording, its version, the date and the address that ticked the box. Article 21 adds that anyone can object to direct marketing at any time, and that this right must be brought to their attention clearly and separately at the latest in the first communication.
Requests to exercise rights get an answer within one month, except in limited cases, according to the CNIL. Rented or bought files are a weak point: the person has to have been informed that their data could be reused and be able to object. Our article on buying an email list details the cost.
Tracking pixels: what changed in 2026
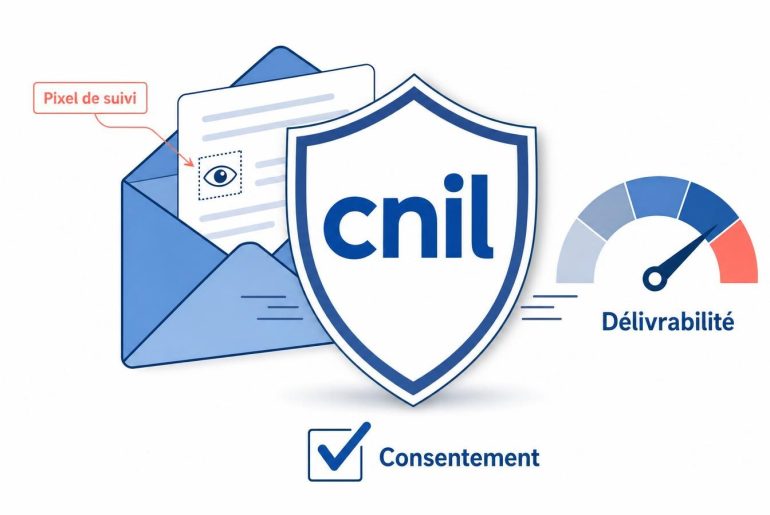
The CNIL adopted its recommendation on tracking pixels in emails on 12 March 2026 (deliberation no. 2026-042) and published it on 14 April 2026; its FAQ followed on 22 July 2026. It applies to every use of trackers in emails, including messages to professional addresses, under article 82 of the Data Protection Act.
Two uses are exempt from consent. A pixel can secure authentication, and a pixel can measure deliverability for one recipient when the email relates to a service they requested, such as an order confirmation or a password reset; the CNIL FAQ indicates a prospecting email sent with prior consent can also count as a requested service. For that exemption the CNIL FAQ presumes the date of last opening to be the only data strictly necessary, used to adjust sending frequency or to stop writing to inactive recipients. Collecting an IP address or a user agent goes beyond that, even if it is anonymised shortly after, unless the sender can document a need.
Outside these cases, the pixel needs valid consent first. The customer exception of L34-5 does not exempt the pixel either: you may be allowed to send the message and still not be allowed to track its opening.
Addresses collected before 14 April 2026 had a transition period. In principle, senders were expected to inform recipients and offer an objection route within three months, by 14 July 2026. The CNIL FAQ allows a reasonable extension where the difficulties are documented. Without the notice, the full rules apply, consent included. Our article on email open tracking and the CNIL explains the effect on open-rate reporting.
What a breach costs
The fine written into L34-5, imposed by the competition and consumer authority, reaches €75,000 for an individual and €375,000 for a company; it is not the only exposure, since the CNIL and Arcep can also sanction. Under article 83(5) of the GDPR, failures on the basic principles of processing, consent conditions included, can reach €20 million or 4% of total worldwide annual turnover, whichever is higher.
The first ceiling stays applicable until the repeal, with one limit. In decision no. 2026-1210 QPC of 25 June 2026, in a case brought by Orange, the Conseil constitutionnel declared three paragraphs of L34-5 unconstitutional because they let three authorities punish the same facts with penalties of the same nature. The repeal takes effect on 31 October 2027. Until then or until a new law, an authority cannot start or continue proceedings under L34-5 if another authority has already prosecuted or definitively sanctioned the same person for the same facts. The prior consent obligation itself was not censured and keeps applying as written.
Mistakes that generate complaints
A newsletter to every visitor who created an account, without a purchase, is the classic one. The CNIL has already held that the customer exception cannot apply without a sale or a service. Others follow: consent bundled into the terms of use, an unsubscribe link that leads to a login page, an unrelated subject line promising a gift, and opening statistics collected from pixels nobody was asked about. Buying a file and mailing it the same week belongs on the list as well: the sender, as controller, must be able to demonstrate consent under GDPR article 7(1), including for people it never met.
Checklist before you send
Run it per campaign, not once a year.
- Is every B2C address backed by a stored, dated consent or by a real prior purchase of a similar product?
- For B2B, does the offer relate to the recipient’s profession, and were they told at collection?
- Does the message show who sends it, with a working stop address and a subject that matches the offer?
- Is the suppression list applied before each campaign, including to imported files?
- Does the pixel collect only what the exemption allows, or is there consent behind it?
- Can you answer a rights request within one month?
List quality after the legal check
Consent says nothing about whether an address still exists. Dead mailboxes bounce, and some abandoned ones turn into spam traps that hurt your sender reputation. Before a campaign, a pass through an email list verification tool removes those addresses; for building a list that holds up, the five-step B2B email list method starts from consent. The detailed handling of proof and unsubscribes stays in our GDPR email marketing guide.